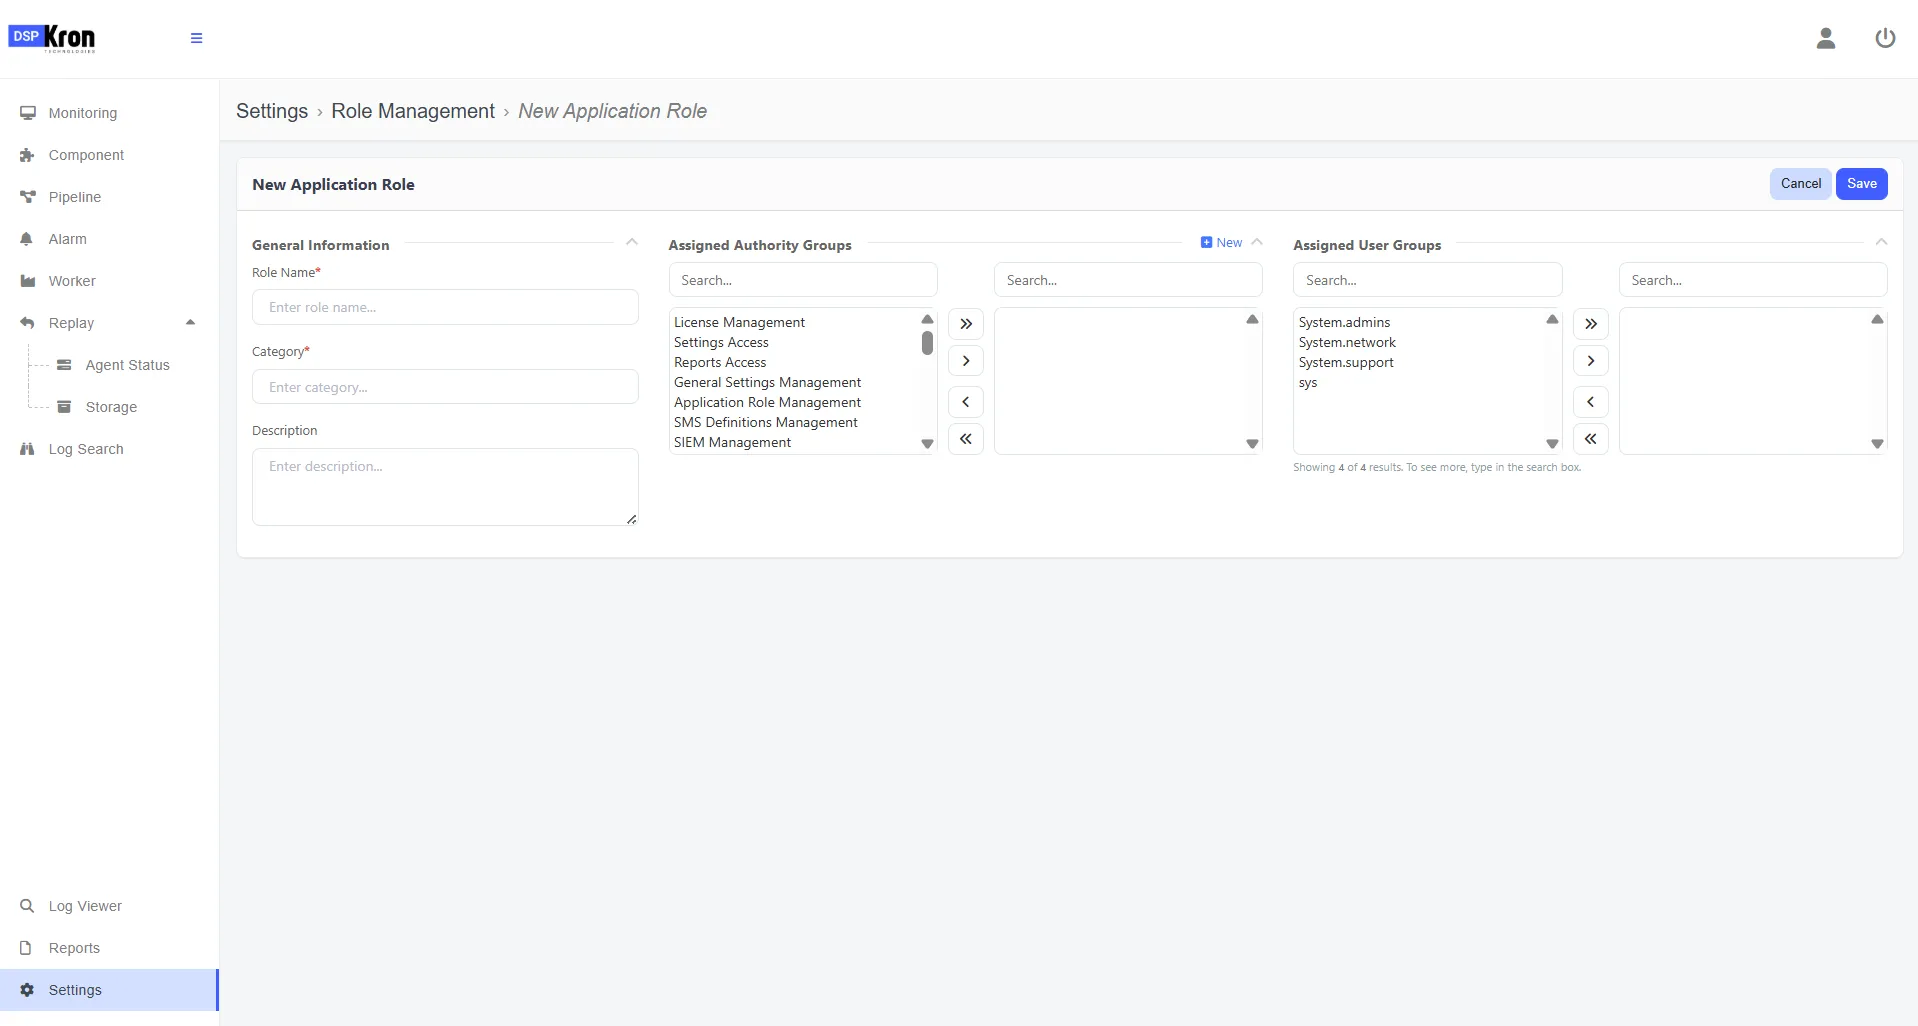
Role Management
It is possible to limit the UI components so that different users can view different functions based on the profile assigned.
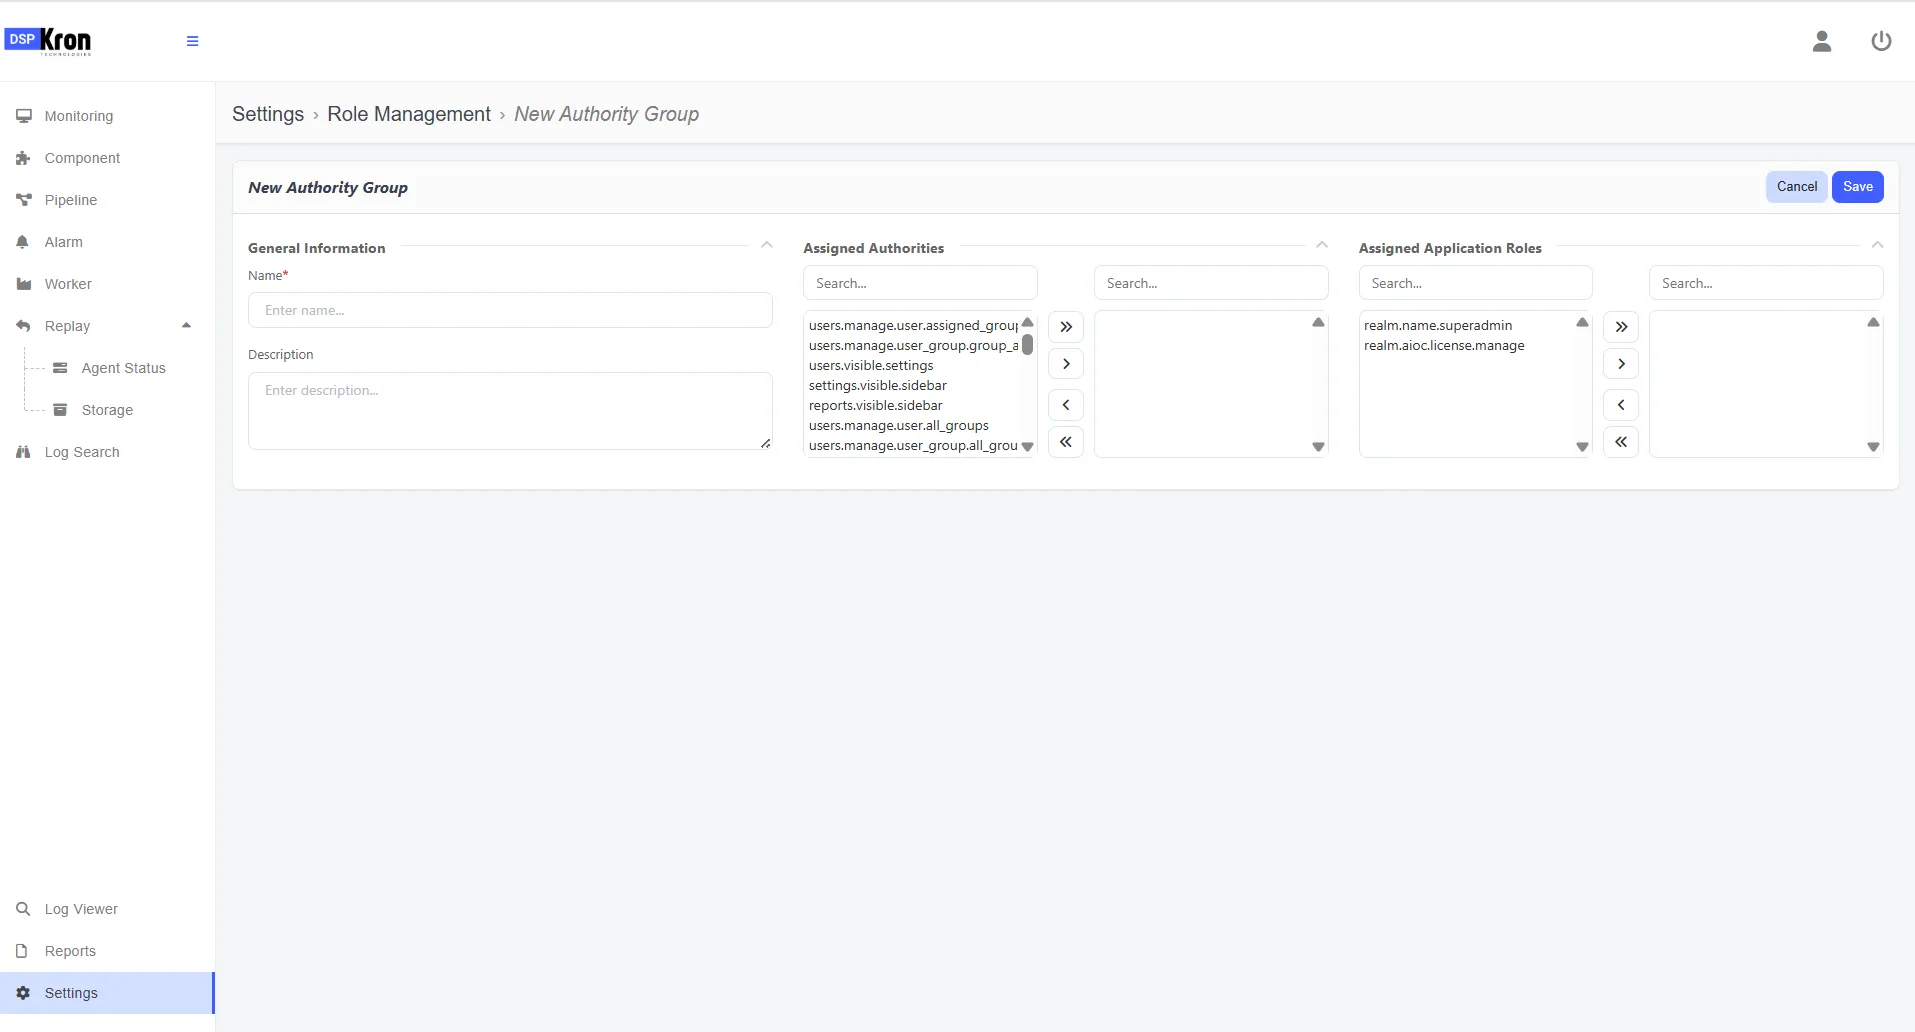
First a Authority Group must be created. Authorithys are the UI functions. These are matched with Roles creates an Authority group.
Authority Groups matching with User groups creates the Application roles. With these roles limited access to non-admin user can be assigned.