Denial-of-Service (DoS) Protection
3 min
Kron DAM includes built-in rate-limiting logic to detect and mitigate Denial-of-Service (DoS) attempts and volumetric anomalies. This mechanism restricts excessive query activity based on IP-specific or global network thresholds and operates at the SQL proxy or agent layer without impacting normal traffic.
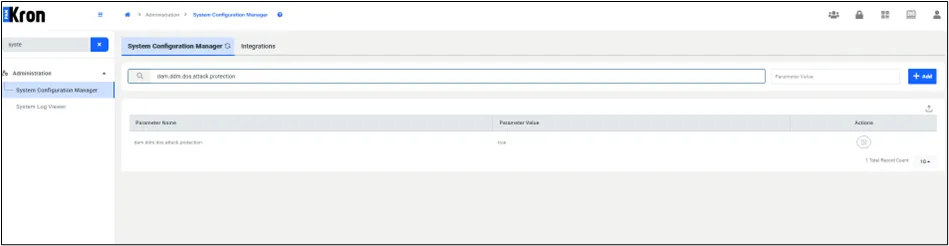
The feature is disabled by default. To enable DoS protection, the following master parameter must be set:
- dam.ddm.dos.attack.protection=true
Once enabled, rate enforcement follows these rules:
- Per-IP Rate Limit is only applied when explicitly enabled by setting the relevant parameter.
- All-Network Rate Limit is always active when protection is enabled, regardless of whether a custom value is supplied.
Parameter | Description | Default (if defined) |
|---|---|---|
dam.ddm.query.rate.limit.from.single.ip | Maximum number of queries allowed per second from a single client IP | 100 |
dam.ddm.query.rate.limit.from.all.network | Aggregate maximum query rate per second from all IPs | 1000 |
If a threshold is exceeded:
- Immediate action – The SQL proxy discards every query that would cause the active rate limit to be violated.
- Persistence of block – An offending client IP remains blocked until the proxy service is restarted or the protection parameters are disabled; the list is held only in memory and is cleared at restart.
- it is visible only in the proxy’s application.log file.
- Setting dam.ddm.dos.attack.protection=false (bypasses the entire mechanism, leaving the environment unprotected).