Fluent
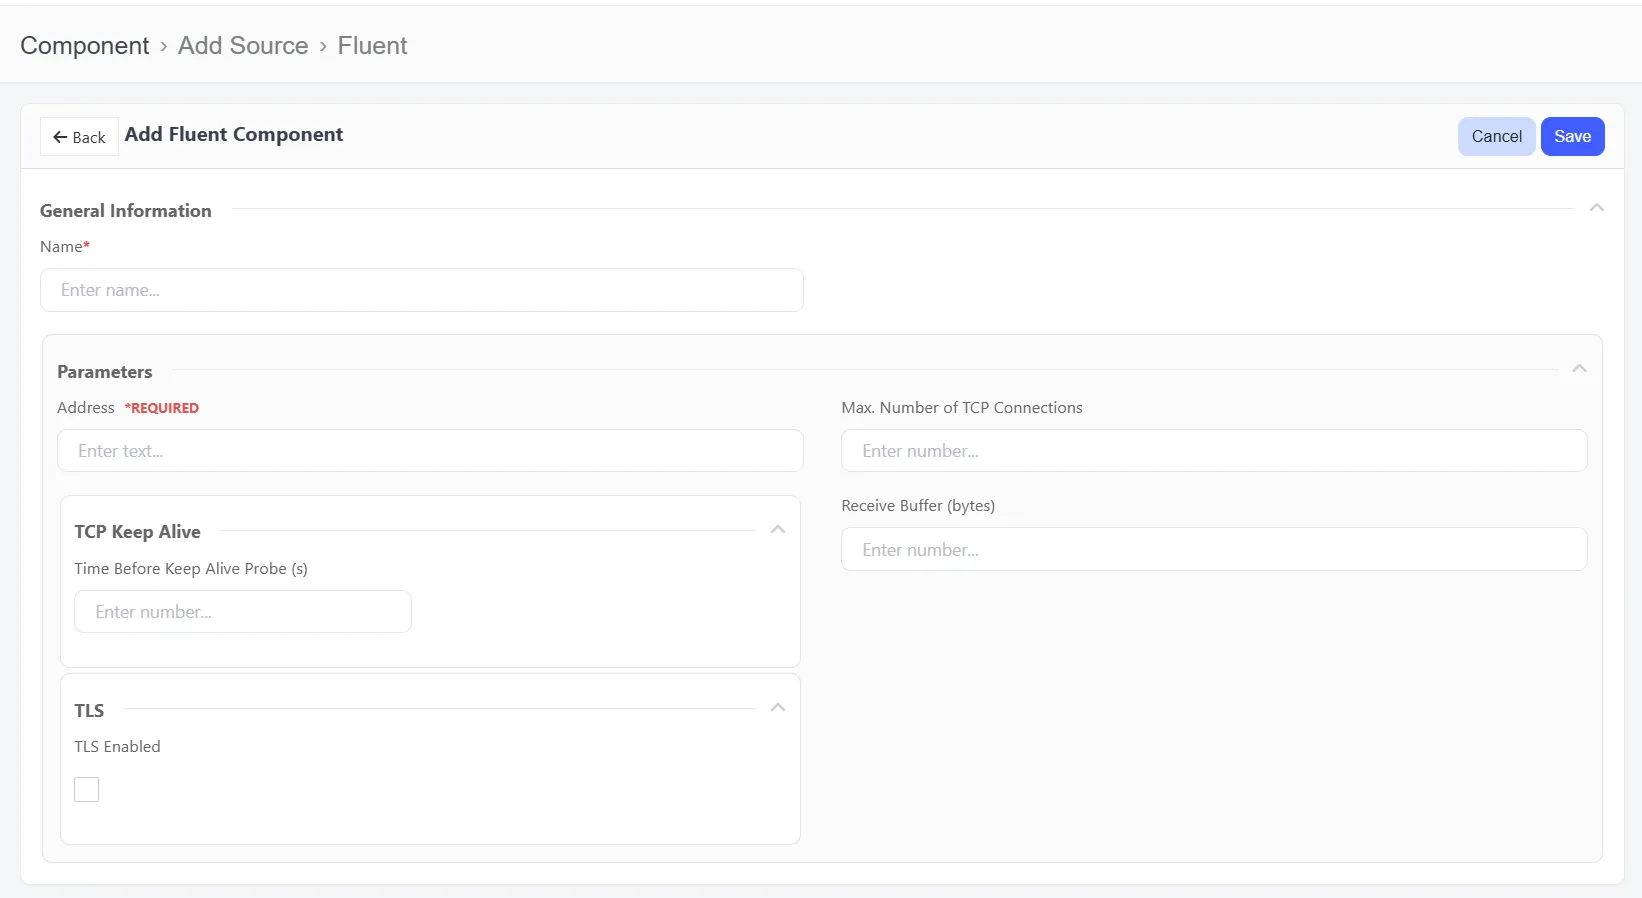
📍 Connection Basics
- address (required, string)
The socket address to bind to and accept connections.
Supports direct socket addresses (must include a port) or systemd#{N} if using systemd socket activation.
Example: 127.0.0.1:8080 or systemd#0
- connection_limit (optional, uint)
Sets a hard limit on how many TCP connections can be active simultaneously.
Useful for controlling resource usage during high traffic.
- receive_buffer_bytes (optional, uint)
Buffer size (in bytes) used per connection for incoming data.
Usually doesn't require customization.
Example: 8192
- permit_origin (optional, [string])
List of allowed IPs or networks (in CIDR format) for connection.
Acts as an access control mechanism.
Example: `["10.0.0.0/8", "192.168.1.0/24"]
♻️ TCP Keepalive Settings
- keepalive.time_secs (optional, uint)
Number of seconds to wait before sending TCP keepalive probes on idle connections.
Helps detect and close dead connections proactively.
🔐 TLS (Transport Layer Security)
TLS configuration for encrypting connections and optionally extracting client certificate metadata.
- tls.enabled (optional, bool)
Enables TLS encryption.
Required if secure communication is needed.
For incoming connections, a server certificate must also be configured (tls.crt_file, tls.key_file).
- tls.ca_file (optional, string)
Path to a CA certificate file used to verify client certificates.
Format: PEM or DER. Can be inline as PEM.
- tls.crt_file (optional, string)
Path to the server's certificate file.
Required for secure (TLS) incoming connections.
PEM, DER, or PKCS#12 supported.
If not using PKCS#12, tls.key_file must also be set.
- tls.key_file (optional, string)
Path to the server's private key file.
Must be in PKCS#8 (PEM or DER) format.
- tls.key_pass (optional, string)
Passphrase for unlocking an encrypted private key file.
Only used if tls.key_file is set and encrypted.
- tls.alpn_protocols (optional, [string])
List of ALPN protocols (Application-Layer Protocol Negotiation) to advertise.
Prioritized in the order given.
- tls.client_metadata_key (optional, string)
If set, client certificate metadata will be added to each event using this key.
- tls.server_name (optional, string)
Sets the server name for SNI (Server Name Indication).
Relevant only for outgoing TLS connections.
- tls.verify_certificate (optional, bool)
Enables validation of certificates during TLS handshake.
Validates expiration, chain of trust, and issuer.
⚠️ Disabling this introduces serious security risks.
- tls.verify_hostname (optional, bool)
Verifies that the hostname in the certificate matches the remote host.
Only applies to outgoing TLS connections.
⚠️ Do not disable unless you're sure of the implications.