Preparing the Installation
- Prerequisites
Check whether Secure Boot is enabled before the installation by running the mokutil --sb-state command.
In case Secure Boot is enabled, the WireGuard kernel module might not be loaded during the installation. Please disable it to continue the installation!!! (see Troubleshooting)
Linux CLI | [root@server~]# mokutil --sb-state |
|---|
· The installation must be performed with root privileges (the installation operations run as root).
· Have a plan of which role will be installed on which server. For example, if an RPAM Connector and an RPAM Portal will be installed, note the real IP addresses (outside the WireGuard tunnel) of both servers in advance, since each installation asks for the information of the other side.
The following example values are used throughout this guide:
Description | Example Value |
|---|---|
RPAM Portal hostname/DNS | https://rpam.company.com |
RPAM Portal real (management) IP address | 10.20.40.116 |
RPAM Connector real (management / local) IP address | 10.20.40.115 |
Kron PAM Server IP address | 10.20.40.151 |
WireGuard VPN port (UDP) | 51820 |
RPAM Portal's WireGuard IP address | 10.0.0.1 |
RPAM Connector's (or Kron PAM Server's, for On-PAM) WireGuard IP address | 10.0.0.2 |
(For Failover Scenario) Backup RPAM Connector's WireGuard IP address | 10.0.0.3 |
- Starting the Installer Wizard (run.sh)
Copy the RPAM MTC installation package (rpam-mtc.tar.gz), which can be provided by the support team, to the /pam directory of the target server and extract it. After that, the web wizard can be started with one of the following two methods.
1. Navigate to the /pam directory and extract the package with the tar command. The package is extracted into the /pam/rpam-mtc directory:
Linux CLI | [root@server~]# mkdir -p /pam && cd /pam [root@server pam]# tar -xvf rpam-mtc.tar.gz |
|---|
2. Navigate to the extracted directory:
Linux CLI | [root@server pam]# cd /pam/rpam-mtc |
|---|
The rpam-installer.service file used in Method B below starts the wizard from the fixed path /pam/rpam-mtc/run.sh. If the package is extracted into another directory, Method B does not work unless the ExecStart line of the service file is updated accordingly. Therefore, extracting the package under /pam is recommended.
If the installation needs to be started from scratch (e.g., because of a wrong input or a missing file), extracting the original rpam-mtc.tar.gz package again into a clean directory is recommended.
Method A – Directly with run.sh (practical for test or one-time installations):
1. In the extracted rpam-mtc directory, make the script executable and start the wizard:
Linux CLI | [root@server rpam-mtc]# chmod +x run.sh [root@server rpam-mtc]# ./run.sh start |
|---|
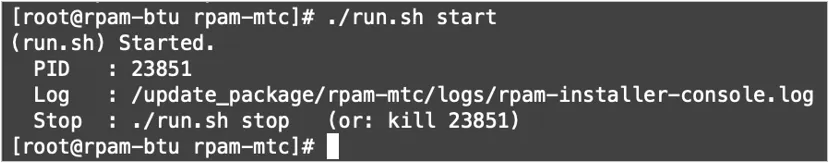
run.sh supports the following commands:
Command | Description |
|---|---|
./run.sh or ./run.sh start | Starts the wizard in the background, prints the PID and the path of the log file, and returns. |
./run.sh stop | Stops the background process by using the PID file. |
./run.sh restart | Runs stop and then start. |
./run.sh status | Reports whether the wizard is currently running, together with the PID and log path. |
./run.sh --foreground | Runs the process in the current terminal (blocking) without sending it to the background. This mode is used by rpam-installer.service; when running manually, start is generally preferred. |
On the first run, run.sh:
· Checks whether python3.11 + venv + pip are working on the system. If they are missing, it installs them from the offline RPM set under files/bootstrap/rpms; if that folder is empty or missing, it automatically tries to install them online with dnf.
· Creates a Python virtual environment (.venv) and installs Flask and its dependencies from the offline packages under files/wheelhouse (or online from PyPI if they are not available).
· Opens the installation port 8443/tcp automatically if firewalld is active.
· Starts the Flask application.
You can verify that the wizard has started successfully with the ./run.sh status command; the output should show "Running (PID ...)" and the path of the log file. The console/startup log is kept in logs/rpam-installer-console.log.
Method B – As a systemd service (persistent; when the wizard should start automatically every time the server boots):
Linux CLI | [root@server rpam-mtc]# cp rpam-installer.service /usr/lib/systemd/system/ [root@server rpam-mtc]# systemctl daemon-reload [root@server rpam-mtc]# systemctl enable --now rpam-installer [root@server rpam-mtc]# systemctl status rpam-installer |
|---|
With this method, the service starts automatically every time the server reboots and is managed with systemctl (systemctl stop/restart/status rpam-installer); there is no need to call run.sh manually.
The wizard does not shut itself down or disable itself after the installation is completed. This is intentional, since the /peer-key page must remain available to update the peer public key even long after the installation (see Section 9).
Check: ./run.sh status (or systemctl status rpam-installer) should show "Running". After that, the wizard should open when http://<server-ip>:8443 is browsed.