Protecting Tokens with MFA
Kron PAM’s built-in MFA can be used as a secondary layer of authentication for logging into the Kron PAM Mobile Client Application for its online features (Approval Management, Geo-Fencing, and Password Manager).
- Admin and user must install the Kron PAM Mobile Client Application and register a token to receive Offline Tokens with the Kron PAM Mobile Client Application. (You get the Offline Tokens from the Offline Token > Add > Register Token menu).
- OTP must be enabled for the user group that will be using MFA for the Kron PAM Mobile Client Application.
To enable MFA for Mobile Application Application:
- Navigate to Administration > System Config. Man.
- Set the mobile.application.otp.enabled parameter as true.
After these settings were done and a login operation was started on the Kron PAM Mobile Client Application, the Kron PAM Mobile Client Application will automatically look for a Registered Token in its Offline Tokens with the name that matched the tfa.otp.issuer parameter. If there is a registered token with another name, then it will prompt the user to change the registered token. The user selects yes and the page forwards to the token page for entering a new token. If the token is matched user can log in. The current six-digit value of the Offline Token is validated with the Kron PAM server, login will be successful.
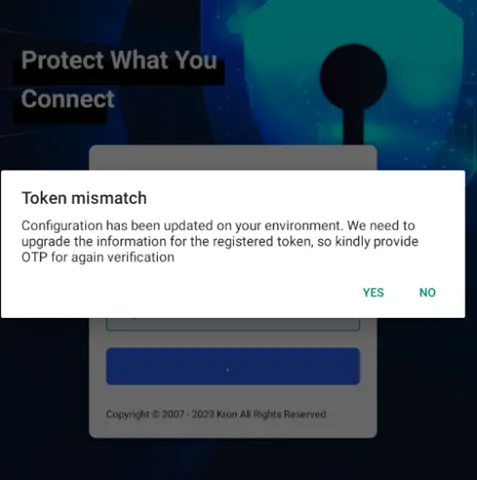
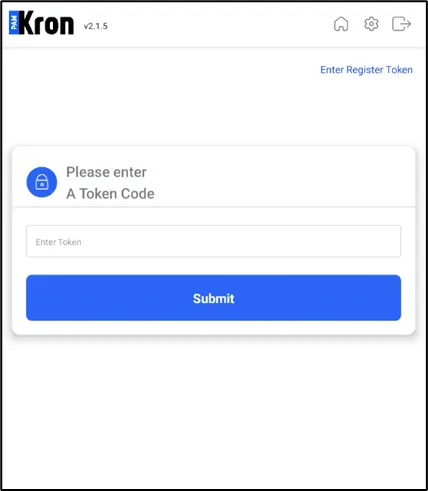
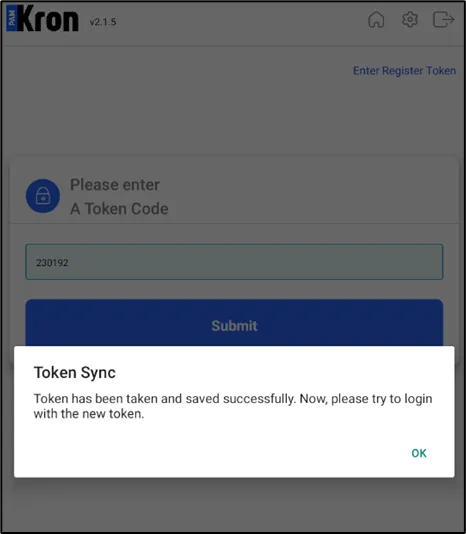
If there’s no Registered Token in the Kron PAM Mobile Client Application and MFA is enabled with the parameter above, registering token also requires a Multi-Factor Authentication. The system will send a one-time password (OTP) user’s phone number. The user will be asked to enter the OTP on the Kron PAM Mobile Client Application.
The Kron PAM Mobile Client MFA functionality works only with the registered tokens to ensure that the offline tokens are only working in one Kron PAM Mobile Client at a time.