2.4.1 Amazon Web Services device import
Importing Devices from Amazon Web Services
The Amazon Web Services (AWS) device import configurations allow Single Connect to automatically detect active instances in a given region and assign the discovered instances to relevant Device Groups based on their custom AWS tags.
The following configuration is required in order to add/discover devices from AWS:
Cloud Integration Configuration for AWS Device Import
- Log in to the Single Connect Web GUI
- Navigate to Cloud Integration
- Set the following fields
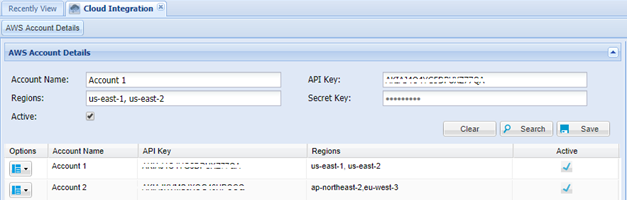
Account Name: Set a desired Account name for the AWS Account to be used for importing devices
API Key: AWS API Access Key ID Secret Key: AWS Secret Key Regions: AWS regions where the devices are located (Multiple regions should be added with a comma (,). Ex: us-west-2, us-east-1, cn-north-1, ap-south-1)
Note |
|---|
The user who has the AWS API access key should have the “AmazonEC2ReadOnlyAccess” permission to import devices. |
Add/Edit Element Type Properties for AWS Devices
Define the "Element Type" properties as shown below, so that Single Connect can identify the OS of the discovered instances.
- Log in to the Single Connect Web GUI
- Navigate to Device Management > Element Type
- Click the “Options” button of the related element type and click “Show Properties”
- Set the “device.import.aws.element.type.pattern”, “device.import.aws.access.protocol”, and “device.import.aws.ssh.username” properties
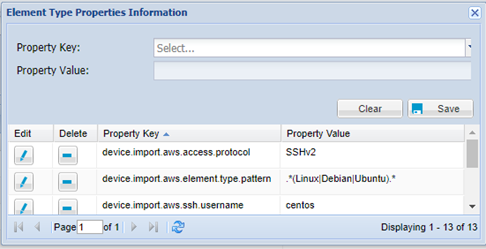
Parameter Name | Parameter Value |
|---|---|
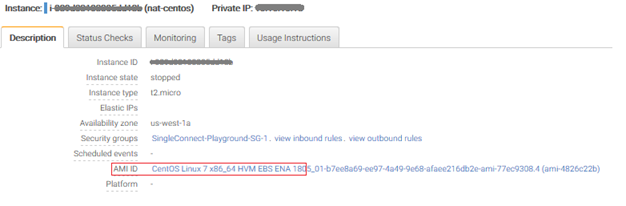
device.import.aws.element.type.pattern | Mandatory. The pattern can be defined as multiple in one element. This pattern is checked against the “AMI ID” description of the instance in order to determine the OS type. |
device.import.aws.access.protocol | Mandatory. This property is used to determine the default access method for the discovered instance. |
device.import.aws.ssh.username | Mandatory. This username is used as the default login credential. |
Note |
|---|
It is necessary to define the new Element Type for each OS type for Single Connect to be able to auto detect. Ex: CentOS Linux, Ubuntu Linux, etc. |
Follow the following steps to import AWS devices having a specific OS to a specific Element Type created for that OS: (The figures given in the below example are for CentOS)
- Log in to the Single Connect Web GUI
- Navigate to Device Management > Element Type
- Create new element type
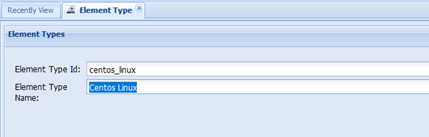
4. Click the “Options” button of the related element type and click “Show Properties” 5. Set the “device.import.aws.element.type.pattern”, “device.import.aws.access.protocol”, and “device.import.aws.ssh.username” properties

Add AWS Devices to specific Device Groups according to their tags
Single Connect imports AWS instances based on their tags. If an AWS instance is to be imported into Single Connect, that instance must have all the tags specified in at least one device group. To create a group with AWS tags:
- Log in to the Single Connect Web GUI
- Navigate to Device Management > Device Groups
- Create a new Device Group, or use an existing Device Group
- Right-click on the Device Group, and select “Show Properties”
- Select the AWS tag property that is matched with devices to be imported
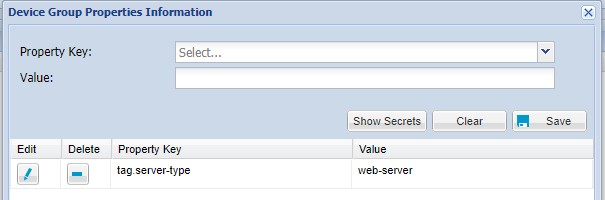
Note |
|---|
Tag values can be written in the regex format. |
Enable AWS Device Import Job
Importing AWS Instances requires a Single Connect Job for synchronization. The job will update the information on Single Connect periodically depending on the cron expression.
- Log in to the Single Connect Web GUI
- Navigate to Device Administration > Job Scheduler
- Click “Fire Job”
- Select “AwsDeviceImportJob” as the Job
- Fill the fields, “Trigger Name”, “Fire Date”, “Cron expression”
- Click on the “Fire Job” button
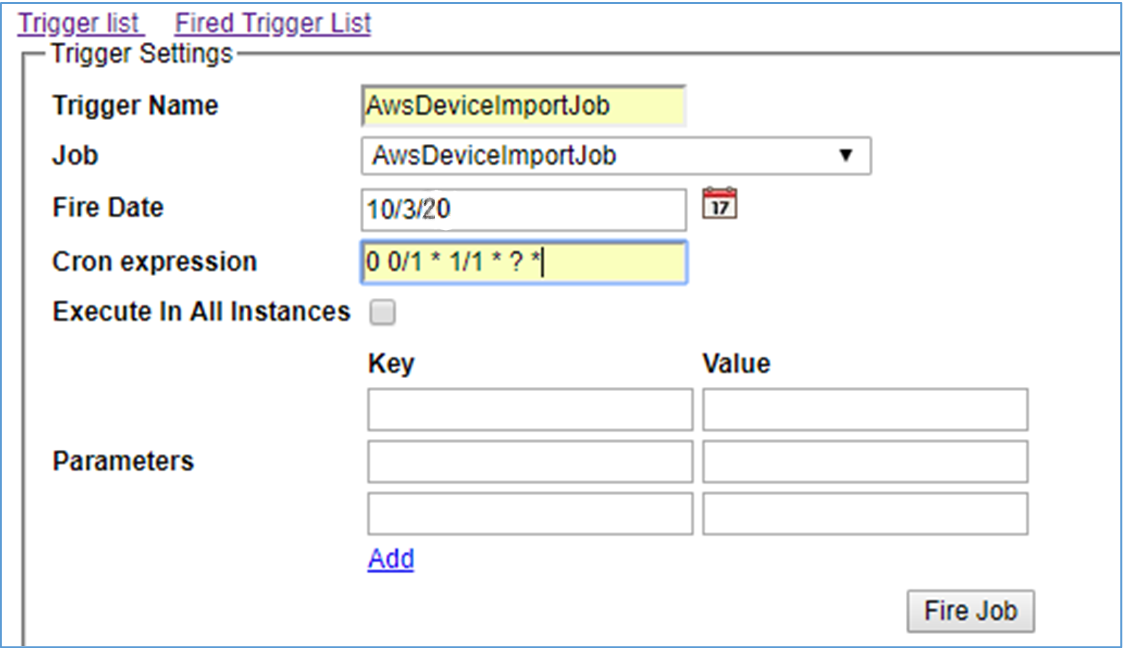
To trigger the job manually, after the job has fired follow the steps below:
- Log in to the Single Connect Web GUI
- Navigate to Device Administration > Job Scheduler
- Click “Trigger List” and then click on “Trigger as Simple Trigger” for the defined “AwsDeviceImport” job
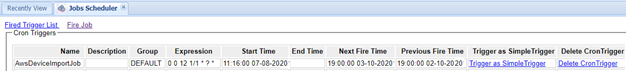
AWS Device List
To list imported devices:
- Navigate to Device Management > Device Inventory
- AWS Devices with specified tags will appear inside the Device Group recently created
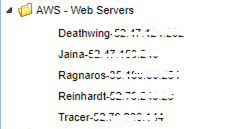
Note |
|---|
AWS Instances are automatically synchronized on Single Connect but the Device Realm and the Policy Realm should be set manually for user accessibility to the devices as well as for policy enforcement.(see also: Managing Devices and Policy Management) |
Configurations for SSH AWS Devices
By default, AWS instances are created with an SSH key in the AWS Console Management. If devices imported from AWS are configured to log in with an SSH key, Single Connect can provide seamless connection to the devices with the SSH keys. Otherwise, the global username and password needs to be defined for each device group. To use an SSH key for AWS devices, follow the steps below:
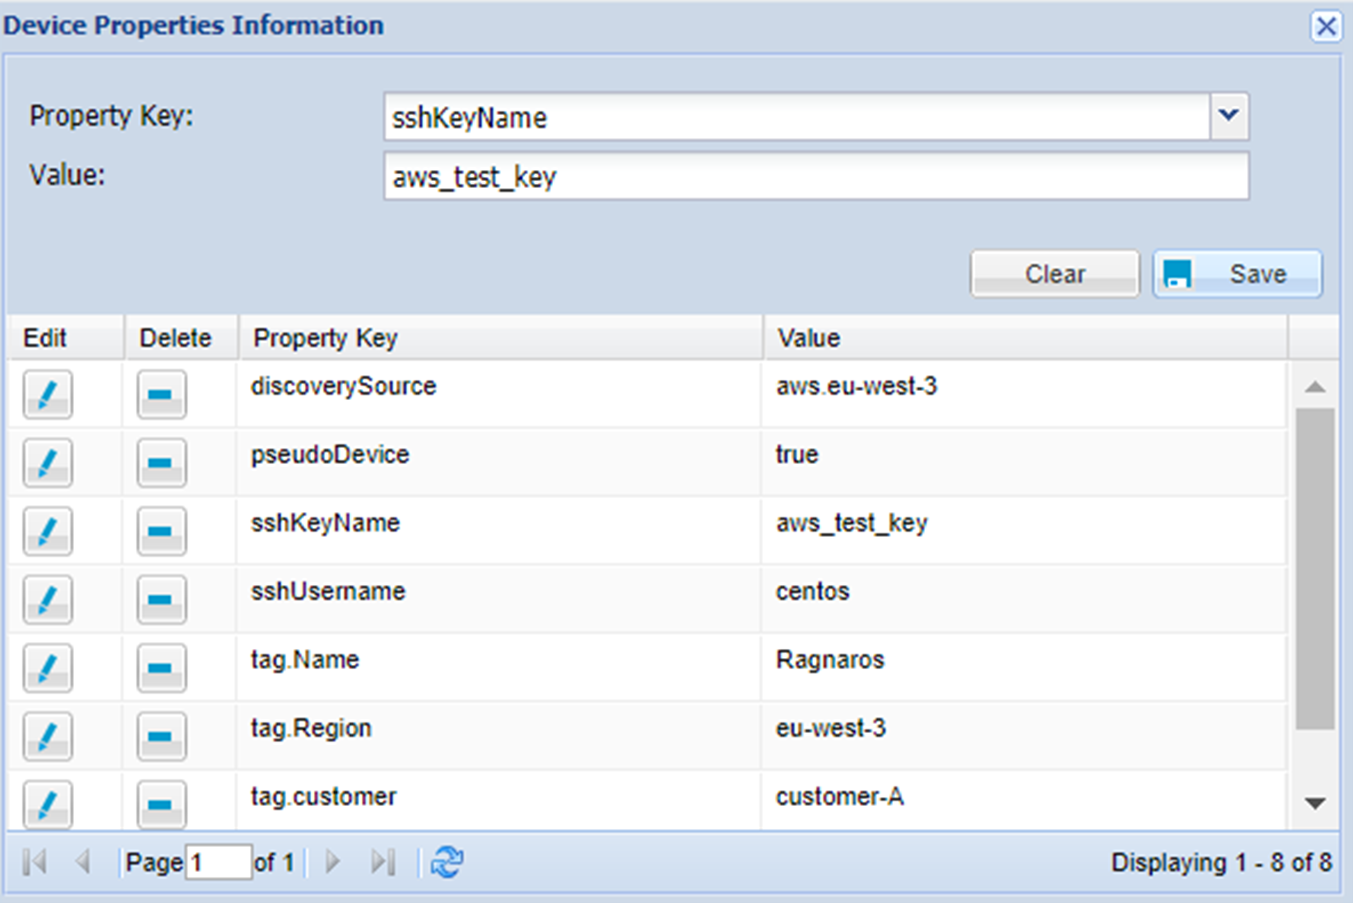
- Get the SSH key name that is stored in the device properties of each device:
- Log in to the Single Connect Web GUI
- Navigate to Device Management > Device Inventory
- Right-click on an AWS Device and select “Show Properties” (The SSH Key name of the device is stored in the “sshKeyName” property.)
- Write down the value of this property to be used for Secret Data Vault module
- Enable SSH Key Connection to Device Groups
- Log in to the Single Connect Web GUI
- Navigate to Device Management > Device Groups
- Right-click on the Device Group in which the AWS devices are imported to and select “Show Properties”
- Select the “addDeviceSshKeyToUserSelection” property and set the value as “true”
- Uploading an SSH key to Single Connect will enable connection to the device:
- Log in to the Single Connect Web GUI
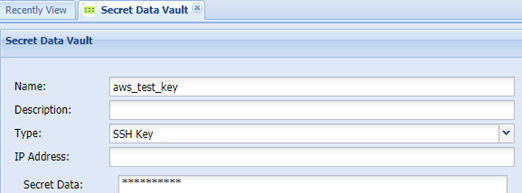
- Navigate to Secret Data Vault > Secret Data Vault
- Fill the required fields.
- The “Name” field must be exactly equal to the value of “sshKeyName” in the Device Property
- Select “SSH Key” for the Type field.
- Copy the contents of your SSH key into Secret Data field.
Note |
|---|
SSH keys must be in an OpenSSH key format. This means that the value put into the Secret Data field should start with the “---- BEGIN SSH2 PUBLIC KEY ----” and end with the “---- END SSH2 PUBLIC KEY ----” indicators. |
SSH Proxy Tag Configuration
Please ask consultation from Kron Technical Support [email protected]