Database Local Account Security Reports
Once a Database Audit job has finished, a separate PDF is generated for every database engine that is present in the configuration (SQL Server, Oracle, PostgreSQL, MySQL). Each PDF follows the same three parts, Inactive Accounts, Expired Accounts and Accounts are not managed by Vault. So the reader can move from a each one of them.
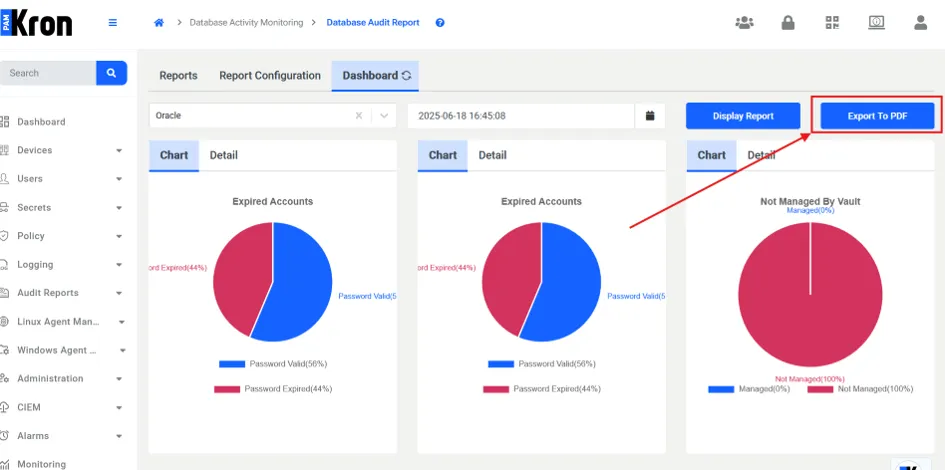
Oracle, MSSQL, PostgreSQL and MySQL have different columns from each other. Below are explanation of each Database.
Microsoft SQL Server – Database Local Account Security Report
Chart | Interpretation | Data Source |
|---|---|---|
Inactive Accounts | The percentage of logins whose last_login value exceeds the inactivity threshold configured in Security ⇒ Policy Settings. | sys.dm_exec_sessions, sys.dm_exec_connections |
Expired Accounts | Logins whose passwords have passed the age defined by the SQL Server password-policy engine (password_expiration_date). | sys.sql_logins |
Accounts Not Managed by Vault | Logins whose credentials are not rotated by Kron PAM Vault (vault enrolment flag is false). | DAM credential inventory |
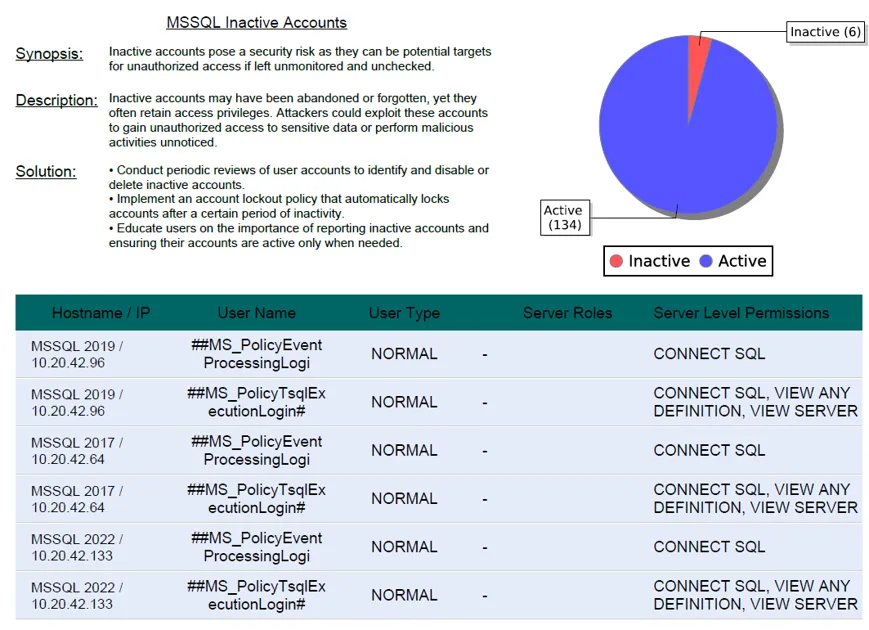
Column | Description | Populated from |
|---|---|---|
Hostname / IP Address | Instance name and listener IP detected by the collector. | Collector metadata |
User Name | Login identifier. | sys.server_principals.name |
User Type | SYSTEM, NORMAL, WINDOWS_LOGIN, CERTIFICATE, etc. | sys.server_principals.type_desc |
Server Roles | Comma-separated roles granted at server scope (sysadmin, securityadmin, …). | sys.server_role_members → sys.server_principals |
Server Level Permissions | Explicit server-scope privileges (CONNECT SQL, VIEW ANY DEFINITION, …). | sys.server_permissions |
Oracle – Database Local Account Security Report
Chart | Interpretation | Data Source |
|---|---|---|
Inactive Accounts | Users whose LAST_LOGIN is older than the inactivity window. | dba_users |
Expired Accounts | Users whose PASSWORD_EXPIRE flag is set or whose password-lifetime has ended. | dba_users, profile limits |
Accounts Not Managed by Vault | Users whose passwords are outside Kron PAM Vault management. | DAM credential inventory |
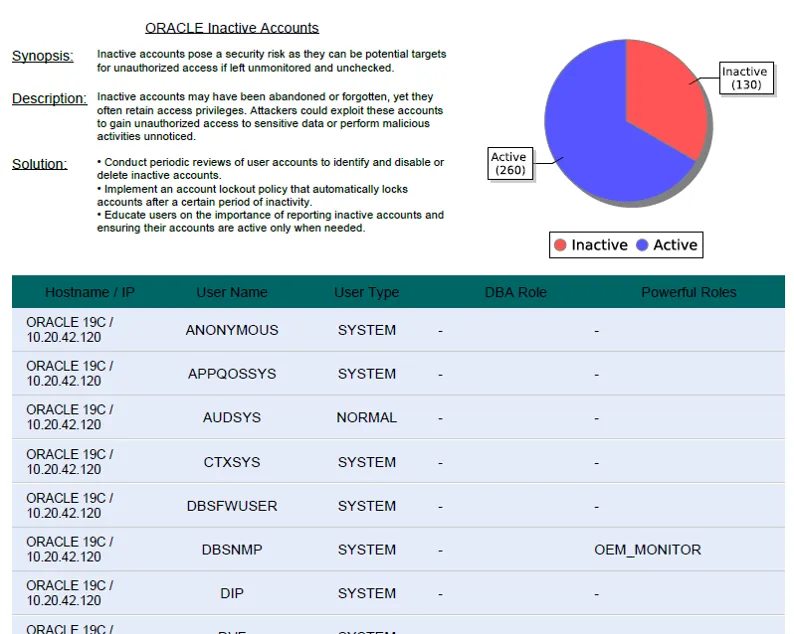
Column | Description | Populated from |
|---|---|---|
Hostname / IP Address | Database service (or SCAN for RAC) plus listener IP. | Collector metadata |
User Name | Oracle user/schema. | dba_users.username |
User Type | SYSTEM, NORMAL, SUPER (for SYS-type accounts). | dba_users.account_status + role check |
DBA Role | Displays DBA when the role is granted, otherwise “–”. | dba_role_privs |
Powerful Roles | Union of high-impact roles (e.g., AQ_ADMINISTRATOR_ROLE, OEM_MONITOR). | dba_role_privs |
PostgreSQL – Database Local Account Security Report
The three charts mirror the MSSQL/Oracle semantics, calculated from pg_authid.rolvaliduntil (expiration) and DAM inactivity tracking.
Column | Description | Populated from |
|---|---|---|
Hostname / IP Address | Server identifier and interface IP. | Collector metadata |
User Name | Role name. | pg_roles.rolname |
User Type | SYSTEM (catalog roles), NORMAL (customer-defined), SUPER (if rolsuper). | pg_roles flags |
Privileges | Aggregated role attributes: superuser, create databases, create roles, replication, can login, inherit rights. | Derived from pg_roles Boolean columns |
No extra paragraphs are appended; all role attributes are compressed into the Privileges column.
MySQL – Database Local Account Security Report
The three charts mirror the MSSQL/Oracle semantics.
Column | Description | Populated from |
|---|---|---|
Hostname / IP Address | Server identifier and interface IP. | Collector metadata |
User Name | Role name. | mysql.user.User, mysql.user.Host |
User Type | Aggregated role attributes: superuser, create databases, create roles, replication, can login, inherit rights. | Flag and name inspection in mysql.user |
No extra paragraphs are appended; all role attributes are compressed into the Privileges column.