Buffer Overflow Attack Protection
Kron DAM implements buffer overflow protection at the SQL proxy layer by validating incoming request sizes. If a request exceeds the defined buffer size limit, it is blocked immediately to prevent potential overflow attacks or abuse patterns such as denial-of-service vectors. The mechanism ensures system resilience against malformed or maliciously large queries.
This feature is disabled by default. To enable buffer overflow protection, set the following master parameter:
Parameter | Description | Default |
|---|---|---|
dam.ddm.buffer.overflow.attack.protection | Enables the buffer overflow protection mechanism. | false |
dam.ddm.buffer.overflow.limit | Maximum allowed request size in bytes. Values below 8192 bytes are not recommended due to minimum metadata requirements. | 65535B |
Behavior and Enforcement
· Every SQL request is evaluated against the dam.ddm.buffer.overflow.limit parameter.
· If the threshold is exceeded, the SQL proxy discards the request immediately.
· The offending client IP is blocked until the proxy service is restarted or the protection feature is explicitly disabled.
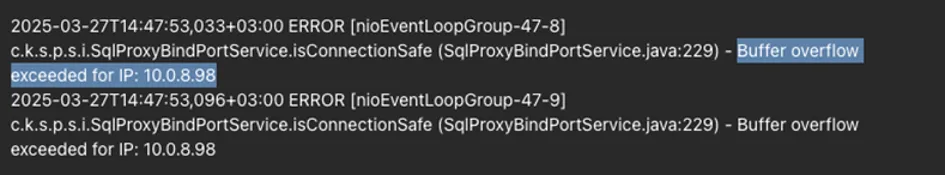
· Block actions are logged exclusively in the application.log file.
· Setting dam.ddm.buffer.overflow.attack.protection=false bypasses this control and exposes the system to buffer overflow risks.