---
title: 5 Two-Factor Authentication
slug: singleconnect-2-16/5-two-factor-authentication
description: Learn how to configure Two-Factor Authentication (2FA) for Single Connect with this comprehensive document. Discover step-by-step instructions on enabling OTP for user groups, managing hardware tokens, and assigning them. Explore how to configure OTP for
docTags:
createdAt: 2020-08-19T15:29:42.000Z
---
This section describes how to configure Two-Factor Authentication.
**Enable OTP**
To active 2FA feature on a user group, follow the steps below
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > 2FA Provisioning
3. Open the “User Group Management” tab
4. Click the “Enable OTP” button of user group
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/fJ8cj0DNuJPt8_2AaKPw1_image.png" size="84" position="center" showCaption="false"}
**Hardware Token Management**
Single Connect users can use a hardware token besides SMS and mobile application for 2FA.
In this case, system admins should import the hardware token seeds to Single Connect.
To import hardware token seeds and assign hardware token to users
1. Log in to Single Connect Web GUI
2. Navigate to Administration > 2FA Provisioning > Hardware Token Management
3. Enter serial number and base32 seed number of hardware token, username of who is assigned, TOTP algorithm.
4. Save configuration to activate hardware token.
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/tTArT5j0IqQLnsav14Nei_1.png" size="84" position="center" showCaption="false"}
System admins can delete assignment of an existing hardware token and delete hardware token from inventory.
**Hardware Token Bulk Import**
To bulk import hardware tokens into the Single Connect inventory, follow the steps below:
1. Log in to Single Connect Web GUI
2. Navigate to Administration > 2FA Provisioning > Hardware Token Management
3. Download the template and fill the downloaded form.
4. Upload the file to Single Connect. Click “Import Token” button to import the hardware tokens.
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/r8qKqDKFO76GhGZTI__H1_1.png" size="84" position="center" showCaption="false"}
**Assign Hardware Token**
Users can assign tokens that have not been assigned to someone before.
User access to this menu should be restricted by the portal functions rules.
To assign hardware tokens, users should follow the steps below:
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > 2FA Provisioning > Assign Hardware Token
3. Enter serial number of hardware token
4. Save configuration.
**OTP System Configuration for Single Connect Web GUI**
To activate OTP for the Single Connect GUI login, follow the steps below:
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > System Config Man.
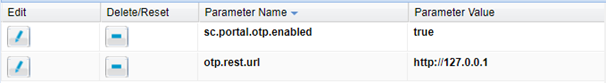
3. Set the required parameters
**sc.portal.otp.enabled=true (one time password enabled for GUI Login)
**
**otp.rest.url= http\://127.0.0.1 **
| **Note** |
| ---------------------------------------------------------------- |
| The rest URL should be set as Single Connect Public IP and port. |
**OTP System Configuration for SSH Proxy**
Please ask consultation from Kron Technical Support
[](https://sc-support@kron.com)**epdestek\@kron.com.tr**
****
**OTP System Configuration for RDP Proxy**
To activate OTP for an RDP connection to target device, follow the steps below:
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > System Config Man.
3. Set the required parameters as;
| ***sc.rdp.connection.otp.enabled=true*** | one time password enabled for RDP connections |
| ---------------------------------------- | --------------------------------------------------------------------------------------------------------- |
| ***sc.rdp.otp.cache.enabled=true*** | If cache parameter activated, user will not be asked for OTP during the cache duration after entering OTP |
| ***sc.rdp.otp.cache.seconds=240*** | cache time in seconds |
| | |
******
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/pV-j1WlUuwkhe8dECe9VG_image.png" size="84" position="center" showCaption="false"}
**Offline/Online Mode Settings**
To adjust 2FA Offline/Online Settings, follow the steps below;
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > System Config Man.
3. Enter in the “Parameter Name” as “2fa” and click the search button
4. Set the value of the “iga.2fa.token.create.count, iga.2fa.token.timestep” parameters
**SMS Settings**
To adjust 2FA SMS Settings, follow the steps below;
1. Log in to the Single Connect Web GUI
2. Navigate to Administration > System Config Man.
3. Enter in the “Parameter Name” as “2fa” and click the search button
4. Set the value of the “iga.2fa.sms.http.body, iga.2fa.sms.http.headers, iga.2fa.sms.http.secret.body, iga.2fa.sms.http.url, iga.2fa.token.create.count, iga.2fa.token.timestep” parameters
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/KP7tTJRNrqG4tUQHTWnER_1.png" size="84" position="center" showCaption="false"}
**2FA Configuration for VPN Services**
Two options available for the VPN 2fa support.
1\. Both the first authentication (with username and password) and the secondary authentication (with OTP) are provided via Single Connect. To activate this feature,
- Define the VPN device according to
- Enable OTP on the User Group (Navigate to Administration > 2FA Provisioning > User Group Management)
2\. Only the second authentication with OTP is provided via Single Connect. To activate this feature,
- Define the VPN device in Single Connect and define the Device Group Realm with related users (See:
- Define element type property in the element type of the VPN device
i. Log in to the Single Connect Web GUI
ii. Navigate to Device Management > Element Type
iii. Click the Options button of the element type and select Show Properties
iv. Set the “radius.auth.only.token.enabled” property with value, “true”
::Image[]{src="https://api.archbee.com/api/presign/g9cApVza9NIhSh0pjZYtA/dCKgKKEWHgJN0LBcLkmBc_image.png" size="50" position="center" showCaption="false"}