Using AAPM Agent on Kubernetes and OpenShift Platforms
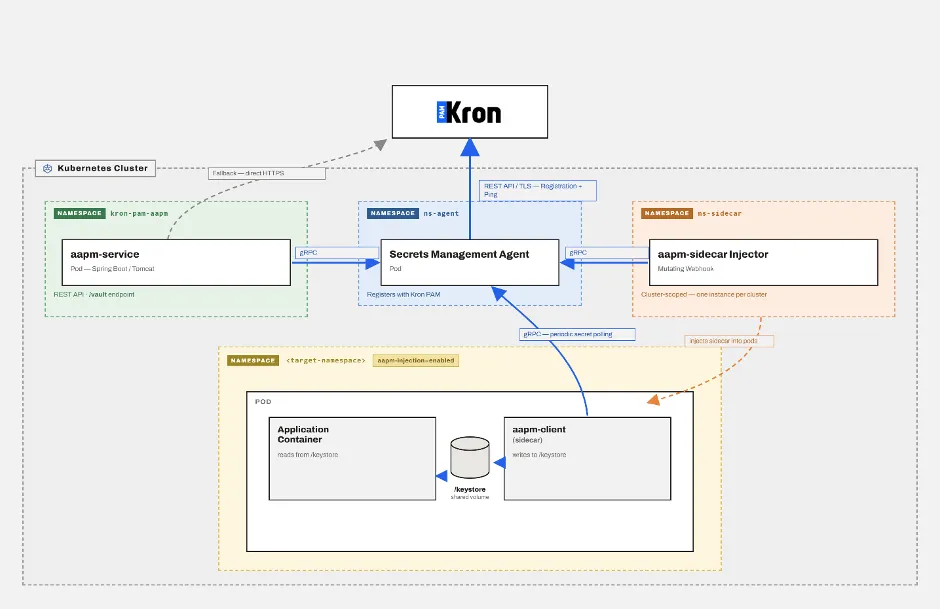
Kron PAM Secrets Management allows applications to retrieve sensitive credentials (passwords, API keys, certificates, and others) at runtime from a central Kron PAM without embedding them in code. The Kron PAM Secrets Management Agent for Kubernetes integration consists of three components:
Kron PAM Secrets Management Agent Components | |
|---|---|
Component | Purpose |
Secrets Management Agent for Kubernetes | The single central bridge between the cluster and the Kron PAM server. It registers with Kron PAM and relays other components' secret requests to Kron PAM. |
aapm-service | An HTTP/REST service for direct secret lookup (/vault endpoint). Used by clients that don't require sidecar injections. |
aapm-sidecar (Injector) | A mutating webhook that automatically adds an "aapm-client" container to pods in labeled namespaces. Periodically fetches secrets and writes them to a file. |